Check one WordPress site for known vulnerabilities, free
Enter a site's address. We read only what the site already shows the public, such as the core version and the plugins and themes named in its pages, and match them against known vulnerabilities.
Sample result
brightspark-electrical.example.com
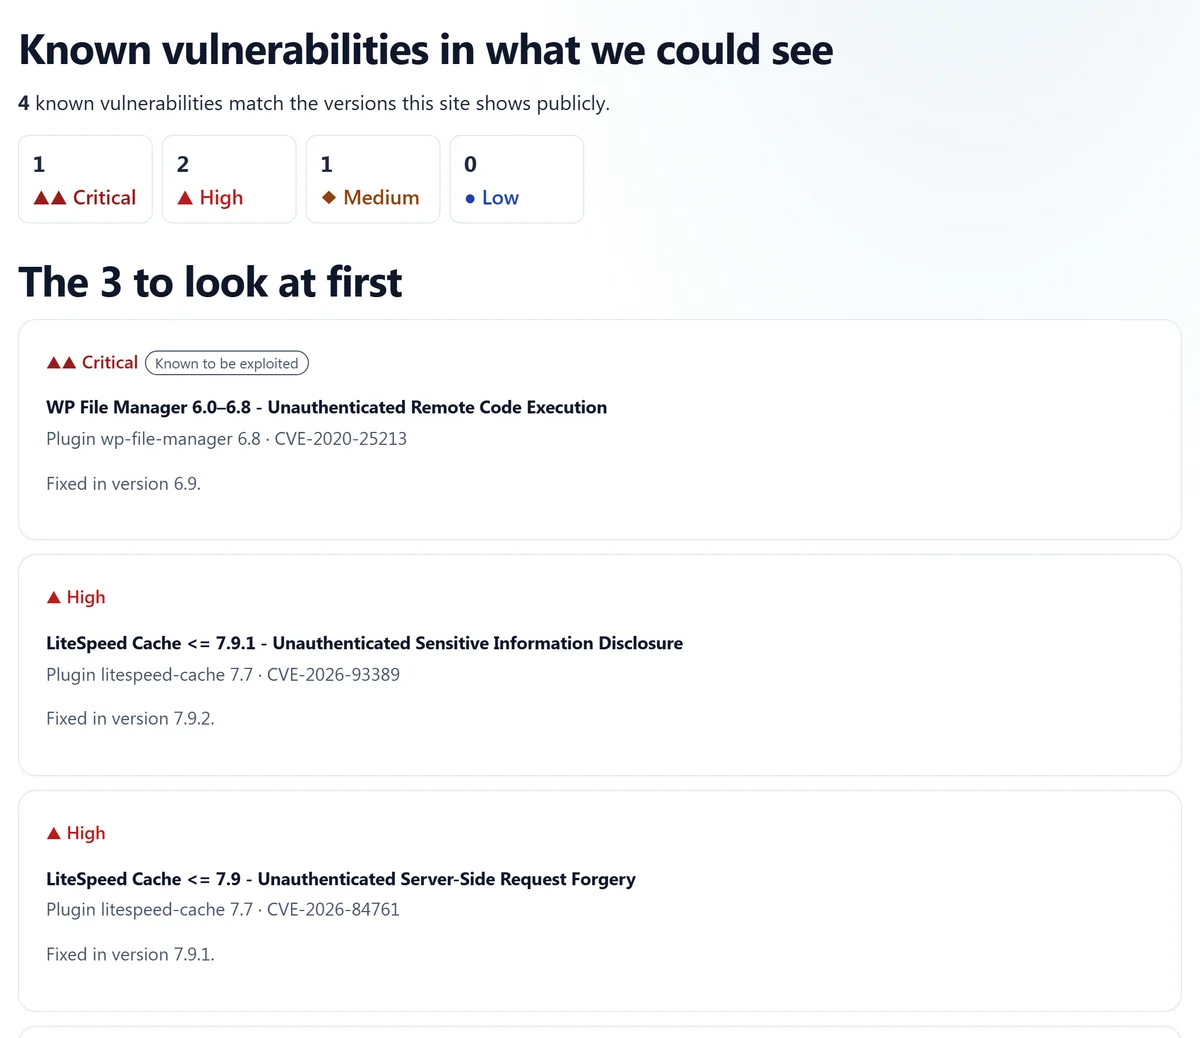
4 known vulnerabilities in what the public pages show. The three to look at first:
- CriticalExploited nowWP File Manager: unauthenticated remote code executionwp-file-manager 6.8 · CVE-2020-25213 · fixed in 6.9
- HighLiteSpeed Cache: sensitive information disclosurelitespeed-cache 7.7 · CVE-2026-93389 · fixed in 7.9.2
- HighLiteSpeed Cache: server-side request forgerylitespeed-cache 7.7 · CVE-2026-84761 · fixed in 7.9.1
What this check does, and doesn't
- Passive only: we fetch the home page and a few public paths, the way a browser would
- No attacks, no login attempts, no load on the site
- Only what's visible from outside: plugins that don't show themselves can't be checked this way
- You see counts by severity and the top findings; the full list comes with a trial
Try it on your own sites
Want every site checked, every day?.
14 days of every Business feature on up to 5 sites. Cancel before it ends and you pay nothing.